Attackers Now Move From Breach to Data Theft in Minutes. Most Enterprise Defenses Are Still Measured in Days.
Executive Threat Briefing · Week ending October 3, 2026
Two NetScaler zero-days exploited for weeks before disclosure. A fifth Cisco SD-WAN zero-day this year. Ransomware that blinds 40 machines in two hours. And Microsoft’s new data says AI has handed attackers the speed advantage. Here is what changed this week, and what to do on Monday.
Executive Summary
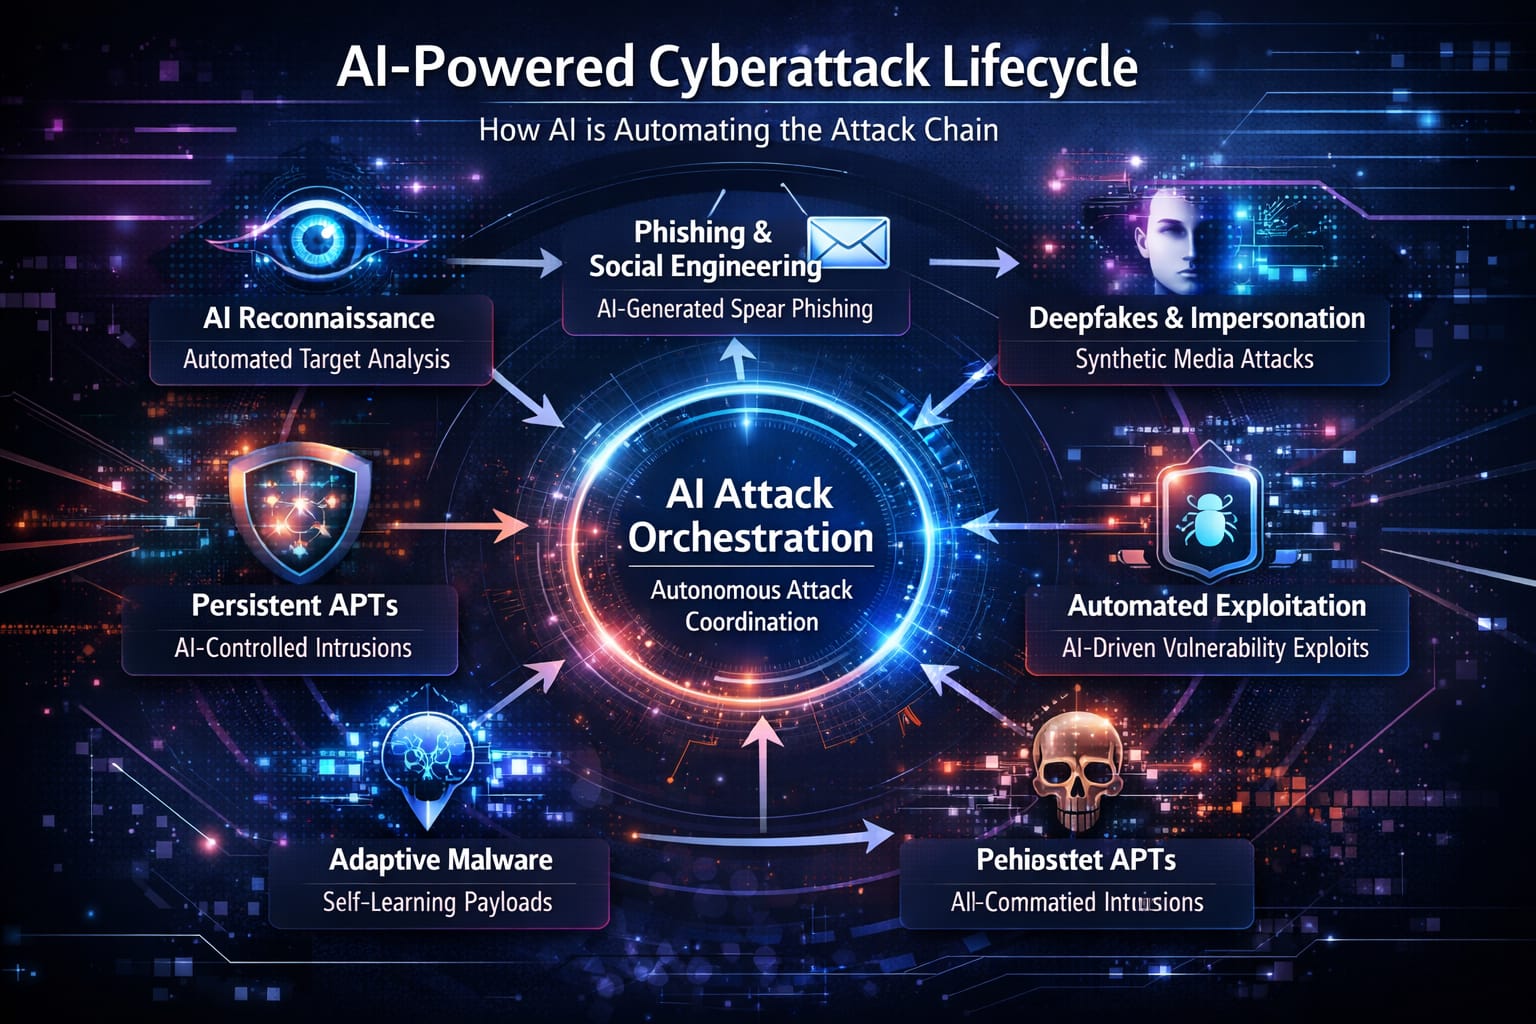
The clock has changed. Microsoft’s 2026 Digital Defense Report, released October 1, says AI has compressed credential discovery, lateral movement and data exfiltration from days to minutes. The median time from a vulnerability being found in the wild to being weaponized is now well under 24 hours.
That would be a warning on its own. This week it came with proof.
Suspected state-sponsored operators exploited a Citrix NetScaler zero-day for roughly three weeks before anyone confirmed it existed. Cisco patched its fifth actively exploited SD-WAN zero-day of 2026. CISA added a critical Fortinet FortiMail flaw to its exploited list. And a China-linked ransomware crew used old SharePoint holes to hit a water utility and a telecom provider.
The common thread is uncomfortable: the devices meant to protect the network are the way in, and patching alone no longer means you are clean.
If your incident response plan assumes you will have a few days, it is already out of date.
| Minutes | Time AI-assisted attackers now need for post-compromise data theft, credential discovery and lateral movement (Microsoft) |
| <24 hrs | Median time from in-the-wild discovery to weaponization |
| ~72,000 | CVEs projected for 2026, a record |
| 7% → 23% | Phishing’s share of incidents as an initial vector, driven by AI-personalized lures |
| ~3 weeks | How long a NetScaler zero-day was exploited before public confirmation |
| 543,000+ | Publicly exposed GitHub credentials reported still active |
Why This Matters to CISOs and Security Leaders
For a decade, enterprise security strategy rested on a quiet assumption: detection buys time. You find the intruder, you contain, you investigate.
That window is closing from both ends.
On the front end, AI is finding and weaponizing bugs faster than organizations can test and ship fixes. Microsoft put it bluntly: remediation is inherently slower than discovery, especially when systems lack the automated testing needed to push changes quickly.
On the back end, once an attacker is inside, the steps that used to take a human operator a long weekend now run in the time it takes to schedule a bridge call.
The question is no longer “Can we detect it?” It is “Can we respond before the data is already gone?”
Microsoft’s own frontline data adds a twist most boards will not expect. AI is not inventing new ways in. User execution accounted for 30% of initial access and valid accounts another 20%. The old doors still work. AI just walks through them faster and at scale.
Which raises the obvious question: what exactly walked through those doors this week?
The Biggest Cybersecurity Developments This Week
1. Citrix NetScaler: the zero-day nobody saw for three weeks
On September 27, Citrix disclosed eight NetScaler ADC and Gateway vulnerabilities and confirmed two, CVE-2026-88771 and CVE-2026-88772 (both CVSS 9.5), had been exploited as zero-days. CISA added both to its Known Exploited Vulnerabilities catalog the same day.
Mandiant and Google Threat Intelligence Group traced exploitation of CVE-2026-88772 back to at least early September, attributing the initial intrusions to advanced, suspected state-sponsored actors. Victims likely span government, financial services, technology, education, and legal and professional services across North America and Europe. Attackers planted web shells, tampered with configurations and tunneled into internal networks.
The executive implication: patching does not remove web shells or invalidate stolen credentials. If your log review starts at the September 27 disclosure, it misses the intrusion window entirely.
2. Cisco SD-WAN: zero-day number five
Cisco patched CVE-2026-76504 (CVSS 9.8), an authentication bypass in Catalyst SD-WAN Manager that lets an unauthenticated attacker gain admin access. Every deployment is affected regardless of configuration, and there are no workarounds. CISA set a federal remediation deadline of October 3.
It is the fifth actively exploited SD-WAN zero-day of 2026, following flaws in February, May and June. For anyone who still treats network management planes as low-risk infrastructure, that pattern is the story.
3. Warlock ransomware hits water and telecom through SharePoint
Symantec reports the China-linked group behind Warlock ransomware (tracked as Longlegs / Storm-2603) is still breaching organizations through on-premises SharePoint flaws. Recent victims include a water utility, a telecommunications provider, a regional government body and a university.
In one critical infrastructure intrusion, the attackers pushed a tool to disable security software on at least 40 hosts in about two hours, then detonated ransomware on at least 33, staging it in the domain’s SYSVOL share so normal replication delivered it everywhere. They used a vulnerable signed driver to kill EDR at the kernel level.
Why CISOs are worried
Warlock’s entry point, the ToolShell SharePoint chain, dates back to mid-2025. More than a year later it still works. The threat is not exotic. It is unfinished patching on servers everyone forgot were internet-facing.
4. A wave of exploited mail, collaboration and DevOps flaws
- Fortinet FortiMail (CVE-2026-104286, CVSS 9.8): unauthenticated arbitrary file write, added to CISA KEV after active exploitation.
- Microsoft SharePoint (CVE-2026-65660): added to KEV after Microsoft confirmed attacks. It requires authentication, which matters little when credentials are already stolen.
- Zimbra (CVE-2026-73570): Microsoft Threat Intelligence detailed exploitation of this unauthenticated command injection to access mailboxes, harvest credentials and exfiltrate data across multiple sectors.
- GitLab (CVE-2026-90970, CVSS 9.9): disclosed October 2 and rated critical. Source code platforms are supply chain infrastructure.
5. AI-themed espionage and policy pressure
China-linked operators impersonated AI experts to phish U.S. policy insiders. In the U.K., MI5 warned that more than 100 academics had contributed to research linked to China’s espionage aims. Meanwhile, Microsoft says it will begin blocking Entra ID script-injection attacks this month, and Apple tightened full-disk access permissions to curb abuse by AI agents.
Individually, each is a patch ticket. Together, they describe a strategy. That is where the real intelligence lies.
Threat Intelligence Breakdown
Read this week’s incidents side by side and three patterns stand out.
The edge is the battlefield. NetScaler gateways, SD-WAN managers, mail gateways. These are appliances that typically cannot run EDR, sit directly on the internet and hold the keys to everything behind them. Attackers know defenders have the least visibility there.
Security tools are now targets, not obstacles. Warlock didn’t evade EDR. It switched it off, at scale, in two hours. Bring-your-own-vulnerable-driver is becoming standard ransomware tradecraft.
Disclosure is the starting gun for everyone else. Once proof-of-concept details surface, opportunistic exploitation follows fast. Mandiant’s CTO expects broad exploitation of the NetScaler flaws by multiple actors.
| Target | CVE | Severity | Priority action |
|---|---|---|---|
| Citrix NetScaler ADC/Gateway | CVE-2026-88771 / 88772 | 9.5 | Patch, then hunt back to early Sept; rotate credentials |
| Cisco Catalyst SD-WAN Manager | CVE-2026-76504 | 9.8 | Upgrade; remove internet exposure; review j_security_check logs |
| Fortinet FortiMail | CVE-2026-104286 | 9.8 | Patch; check for written files and persistence |
| Microsoft SharePoint (on-prem) | CVE-2026-65660 + ToolShell | Critical | Patch; rotate ASP.NET machine keys; hunt web shells |
| Zimbra Collaboration | CVE-2026-73570 | Critical | Patch; audit mailbox access and credential exposure |
Vulnerability & Exploit Analysis
Vulnerability management was built for a world of monthly patch cycles and CVSS-sorted spreadsheets. That world is gone.
With roughly 72,000 CVEs expected this year and weaponization measured in hours, prioritizing by severity score alone guarantees you will be patching the wrong things first. Google researchers add another wrinkle: AI-discovered vulnerabilities are more likely to enable remote code execution, the most dangerous category.
Executive insight: what nobody is talking about
The NetScaler, SD-WAN and FortiMail flaws share one trait: they live on systems that are rarely in the EDR or SIEM coverage map. Your exposure is not your CVE count. It is the number of internet-facing appliances you cannot see inside. Ask your team for that number this week.
The practical shift: KEV-listed and internet-facing comes first, always, followed by anything touching identity. Everything else waits.
AI-Powered Cybersecurity Risks
Microsoft describes a rapid progression over the past six months: from AI assisting human operators, to AI directing attack activity, toward autonomous execution. It cited a campaign called JadePuffer as an example of attackers moving toward fully autonomous operations, and noted research showing AI-driven self-spreading worms are feasible with current technology.
Microsoft also says China, Russia and North Korea are already using AI in real operations, for vulnerability research, tooling, malware development and persona creation. North Korea’s fake IT worker schemes have used deepfake video to get hired at Western firms.
Equally important is what Microsoft did not claim: attacks are not yet fully autonomous, and most AI use still targets specific steps of existing attack chains.
AI hasn’t rewritten the attacker’s playbook. It has put the existing one on fast-forward.
The hidden enterprise risk is your own AI. Every agent with access to email, files and SaaS tools is a new identity with real permissions. Microsoft’s guidance is direct: reduce data oversharing and apply least privilege before rolling out more agents.
Cloud & Infrastructure Security Impact
This week’s exploited systems are hybrid by nature. NetScaler gateways front remote access. SD-WAN managers orchestrate branch connectivity. SharePoint and Zimbra bridge on-premises data with cloud identity.
That makes identity the blast radius. A compromised gateway yields session tokens and credentials that work in the cloud. More than half a million exposed-but-still-active GitHub credentials show how often secrets outlive the incidents that leaked them.
- Cloud security: token theft from edge devices bypasses MFA prompts. Monitor for anomalous session reuse, not just failed logins.
- Supply chain: critical GitLab flaws and the March 2026 compromise of the Axios npm package, attributed to North Korea, keep code pipelines squarely in scope.
- OT and critical infrastructure: Warlock’s water utility victim and new EU proposals for industrial cybersecurity rules signal rising regulatory and physical stakes.
Ransomware & Nation-State Threats
The line between espionage and extortion keeps blurring. Warlock is a China-linked group running ransomware. The NetScaler campaign used espionage-grade tooling before opportunists piled in.
Law enforcement scored a win: Hamburg police identified a suspect they describe as the administrator and main operator of the KillSec ransomware group. But arrests rarely slow the ecosystem for long.
Breach consequences continue to land on consumers too. Japanese car-sharing service Times Car disclosed a breach affecting 6.6 million accounts.
How attackers are adapting
Kill the EDR first. Stage payloads in trusted infrastructure like SYSVOL. Use legitimate tunnels and file-sharing services for command and control. Every step is designed to look like administration, not attack.
Winners and Losers
| Gaining ground | Losing ground |
|---|---|
| Organizations that inventory and monitor edge appliances like endpoints | “Patch and move on” programs that never hunt for persistence |
| Identity security platforms. Palo Alto Networks’ $21.1B CyberArk deal and ServiceNow’s Veza acquisition show where capital is flowing | Static credentials and long-lived secrets |
| AI-assisted SOCs that triage at machine speed; Google is even offering Gemini 4 Argon to vetted defenders | SOCs built around human-speed ticket queues |
| Teams with tamper-protected EDR and driver blocklists | Unpatched on-prem SharePoint, still a ransomware favorite |
One number puts the stakes in context. In PwC’s 2026 Global Digital Trust Insights survey of nearly 3,900 executives, only 6% said they were very capable of withstanding attacks across all vulnerabilities. The other 94% are where this week’s attackers went shopping.
What Security Leaders Should Do Next
These steps are ordered by urgency.
- Close this week’s KEV items within 72 hours. NetScaler, Cisco SD-WAN Manager, FortiMail, SharePoint and Zimbra. Confirm, don’t assume.
- Hunt, then declare clean. For NetScaler, review logs back to early September. Look for web shells, modified configs and unexpected tunnels. Patching doesn’t evict an attacker.
- Rotate what may have been exposed. Credentials, session tokens and SharePoint ASP.NET machine keys on any system that was vulnerable.
- Pull management planes off the internet. SD-WAN managers, appliance admin interfaces and mail gateway consoles belong behind allow-lists.
- Harden EDR against tampering. Enable tamper protection, enforce vulnerable-driver blocklists and alert when agents go silent on multiple hosts.
- Re-time your incident response plan. Tabletop a scenario where data leaves in 30 minutes. Pre-authorize containment actions so no one waits for approval.
- Govern your AI agents as identities. Inventory them, scope their permissions and fix data oversharing before expanding deployments.
Brief your board in one sentence
“Attackers can now move from first access to data theft in minutes, so we are prioritizing internet-facing systems, identity and response speed over everything else.”
The Future of Enterprise Cybersecurity
What happens next is not hard to predict. Expect broad, opportunistic exploitation of the NetScaler flaws. Expect more edge-device zero-days, because they keep paying off. And expect AI to keep pulling the timeline forward, for attackers first and defenders second.
The billion-dollar shift is already visible in deal flow: consolidation around identity, AI-native security operations and protection for AI agents themselves. Microsoft frames it as AI changing the physics of cybersecurity. Defense now has to operate at machine speed, with humans setting policy rather than clicking through alerts.
How competitors are already modernizing: the organizations pulling ahead treat every appliance as an endpoint, every agent as an identity and every minute of dwell time as a measurable business cost.
Final Executive Takeaway
This was not a week of exotic threats. It was a week of familiar weaknesses exploited faster and more quietly than most defenses are built to handle.
The organizations that come through the next twelve months intact won’t be the ones with the most tools. They will be the ones that see their edge, lock down identity and respond in minutes.
The attackers have already made that adjustment. The only question is how long your team takes to make theirs.
Frequently Asked Questions
What are the most critical cybersecurity threats for enterprises right now?
As of early October 2026, the most urgent are actively exploited zero-days in Citrix NetScaler (CVE-2026-88771 and CVE-2026-88772), Cisco Catalyst SD-WAN Manager (CVE-2026-76504) and Fortinet FortiMail (CVE-2026-104286), plus continued ransomware exploitation of on-premises SharePoint.
How is AI changing cyberattacks?
Microsoft’s 2026 Digital Defense Report says AI has cut post-compromise steps such as credential discovery, lateral movement and data exfiltration from days to minutes, and pushed median time to weaponization below 24 hours. Attacks are not yet fully autonomous.
Does patching the Citrix NetScaler zero-days remove the threat?
No. Patching closes the vulnerability but does not remove web shells, configuration changes or stolen credentials. Organizations should hunt for compromise back to early September 2026 and rotate credentials.
What should CISOs prioritize in vulnerability management?
Prioritize vulnerabilities on CISA’s Known Exploited Vulnerabilities list that affect internet-facing systems, then anything tied to identity. CVSS score alone is no longer a reliable ordering method.
How do ransomware groups disable EDR?
Groups like Warlock use bring-your-own-vulnerable-driver (BYOVD) techniques, loading a legitimately signed but flawed driver to terminate security processes at the kernel level. Tamper protection and driver blocklists reduce this risk.
Sources include Microsoft’s 2026 Digital Defense Report, Mandiant/Google Threat Intelligence Group, Rapid7, Symantec, Cisco and CISA advisories, PwC, SecurityWeek, BleepingComputer, Help Net Security, Infosecurity Magazine and The Hacker News. CVE details current as of October 3, 2026; check vendor advisories for the latest fixed versions.