


Latest in Cybersecurity news
Binance’s $6.34 Billion Hack Began With a Fake Job Interview. Your Developers Are Next.
Binance’s incident report shows the record theft did not need a zero-day. A trojanized installer, a …
WordPress Core CVE-2026-119977: Update Before the Upgrade Window Becomes an Open Door — Federal Deadline November 6
CISA added WordPress Core CVE-2026-119977 to its Known Exploited Vulnerabilities catalog on November…
Aur0ra Ransomware’s AI Agents Reached Domain Admin: What Every CISO Needs to Know
A ransomware crew handed the keyboard to an AI agent—and watched it reach domain admin faster than m…
NordVPN Review 2026: 6 No-Logs Audits, Speed and Real Price
Is NordVPN worth it in 2026? Its no-logs policy has now passed six independent audits, the Basic pla…
Ivanti CVE-2026-111357: The Root Fix October Missed, Due Today
Ivanti has patched the two Connect Secure zero-days its October fix left open. CISA’s deadline for C…
Edge-Device Zero-Days of October 2026: 12 Exploited, 1 Due Sunday
October 2026’s edge-device zero-days: 12 exploited products from Fortinet, Cisco, Citrix, Ivanti and…
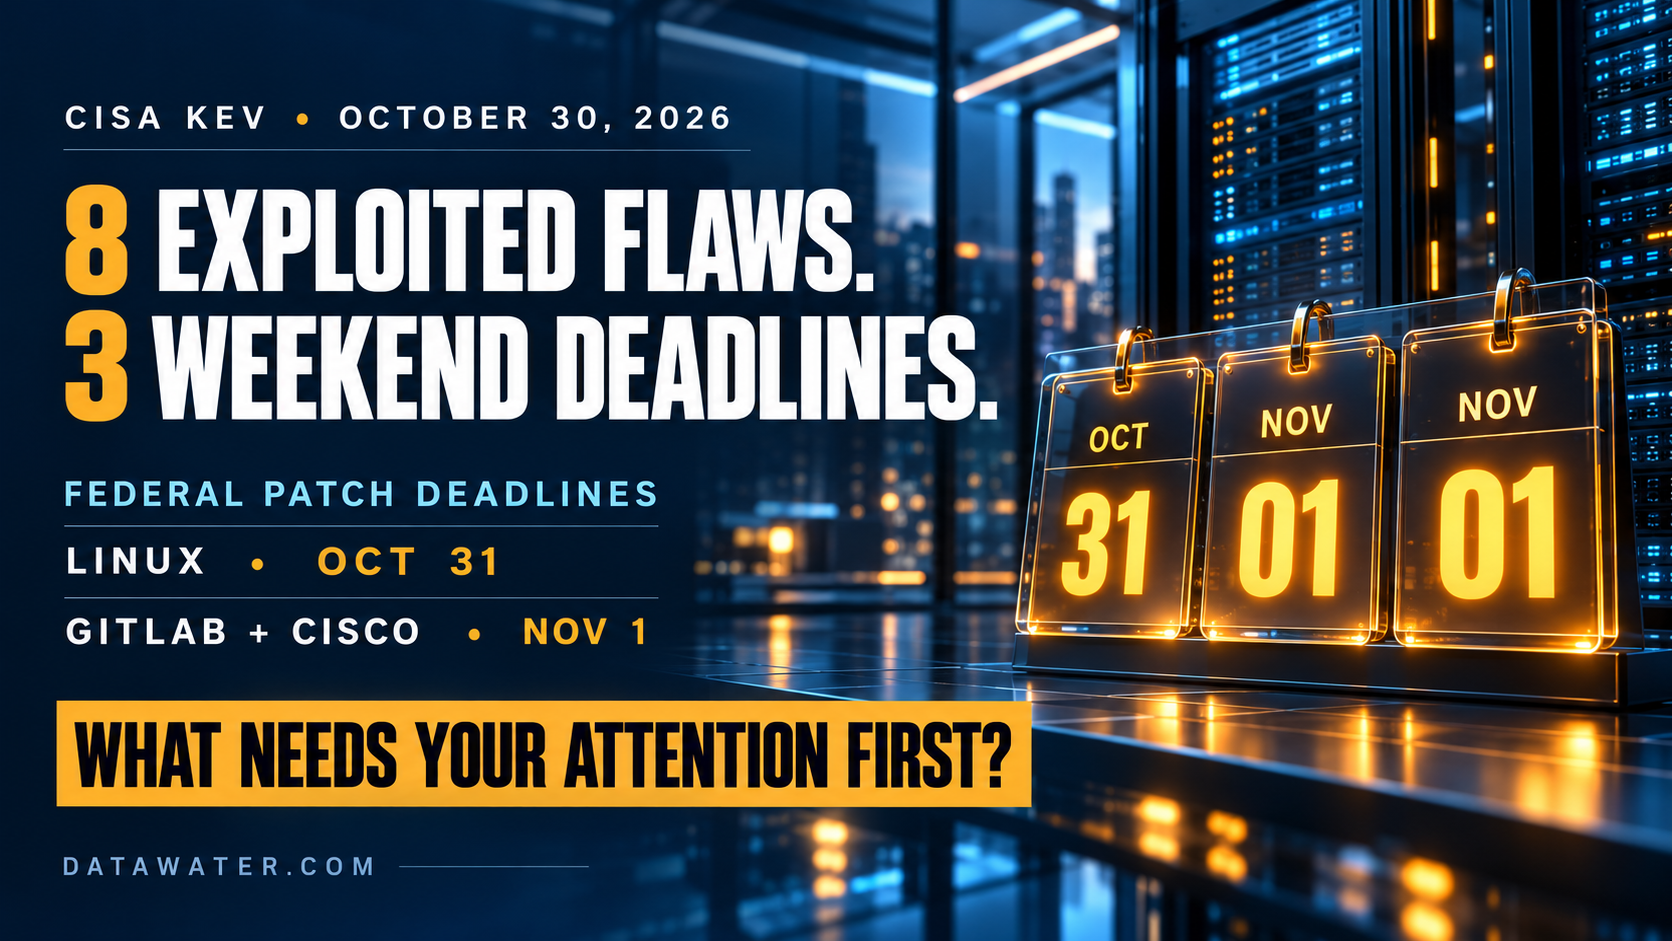
CISA KEV Weekly Roundup: 8 Exploited Flaws, 3 Due This Weekend
CISA added eight exploited flaws to KEV this week: PHP, Adobe Commerce, Brotli, the Linux kernel, VM…
Fragnesia CVE-2026-46300: Linux Root Bug Now Exploited, Due Saturday
Fragnesia, the Linux kernel root bug disclosed in May, is now being exploited. A suspected China-nex…
Tenable Free Trial: Nessus and Tenable One Compared (2026)
Tenable offers free trials of Nessus Professional, Nessus Expert and Tenable One Vulnerability Manag…